

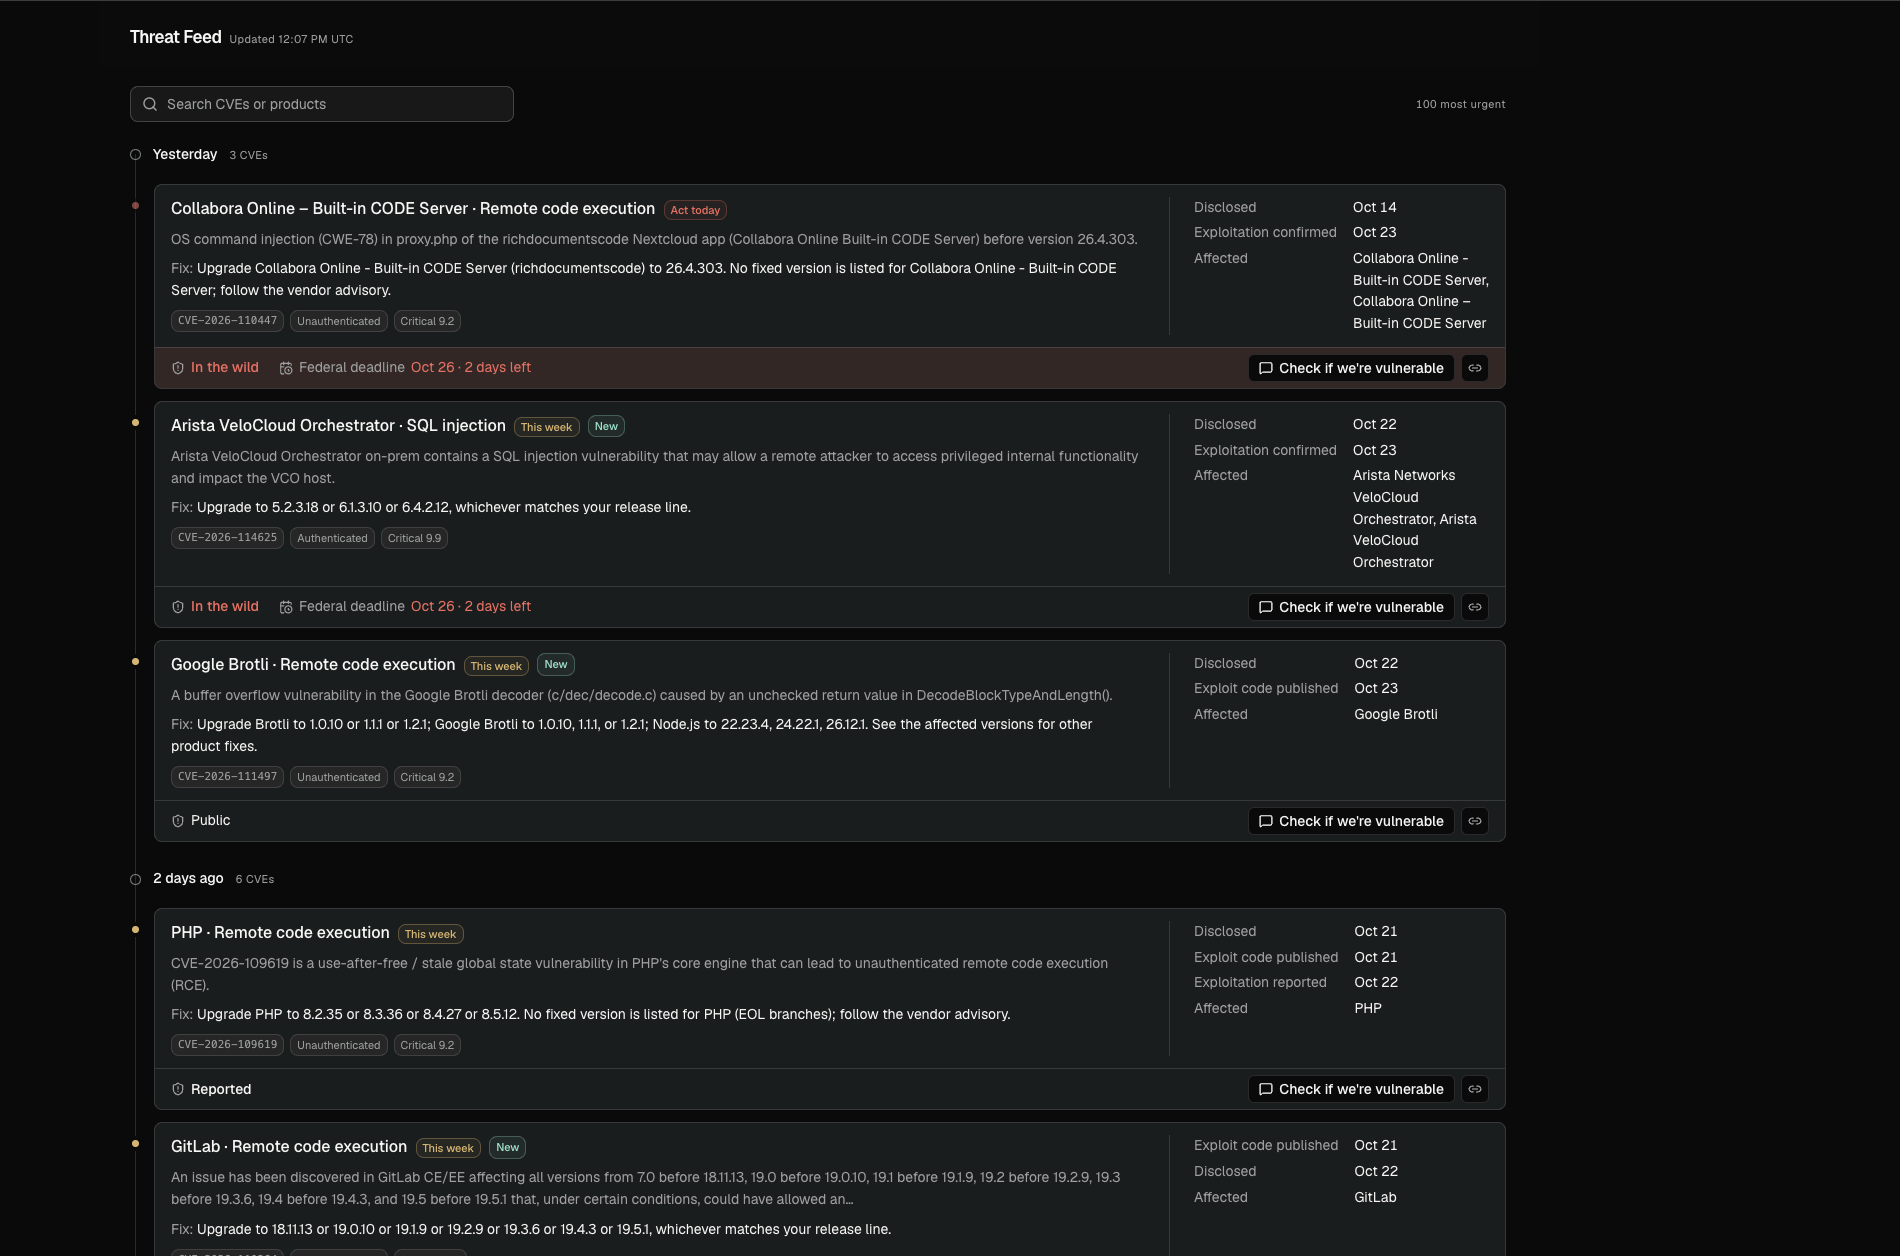
What’s in the feed
The feed shows the 100 most urgent CVEs and refreshes every five minutes. Enclave ranks them by:- Exploited: confirmed by CISA or the EU Vulnerability Database, or seen by honeypots in the last 30 days.
- Breaking: new, critical, and reachable over the network without credentials.
- Trending: discussed this week in security news, social media, Hacker News, and GitHub.
Read a card
Each card shows the affected product, a summary, the fixed version, and a timeline.
Cards can also show Ransomware, New, and the US federal patch deadline when CISA lists the CVE as exploited.
Click a CVE’s title to open its page with the full timeline, affected versions, fix, and sources.
Search and filter
Search by CVE ID or product, or filter by time. Search covers every CVE in the latest refresh, not just the 100 shown. To link to one CVE, use/threat-feed?cve=<CVE-ID>.
Check if we’re vulnerable
Click Check if we’re vulnerable on a card or CVE page. Enclave opens a Research session and:- Works out where the affected software could run.
- Tells you what it can and can’t see, and offers to connect what’s missing.
- Checks your repositories, organization graph, cloud accounts, and servers in parallel.
- Answers with a verdict: Affected, Not found in what I checked, Not affected, or Can’t tell yet, plus what to fix first.